The VIP list vs the bouncer's ban list
The great Blizzard DNS rebinding bypass
When video players go rogue
The whitelist in your daily digital life
YOUR GOAL
Master of Securing the world with the whitelist fix
007skaty Principle of Least Privilege
Say no by default and only let the whitelist through.
007skaty Hidden protocols inside the FFmpeg video engine create serious security risks.
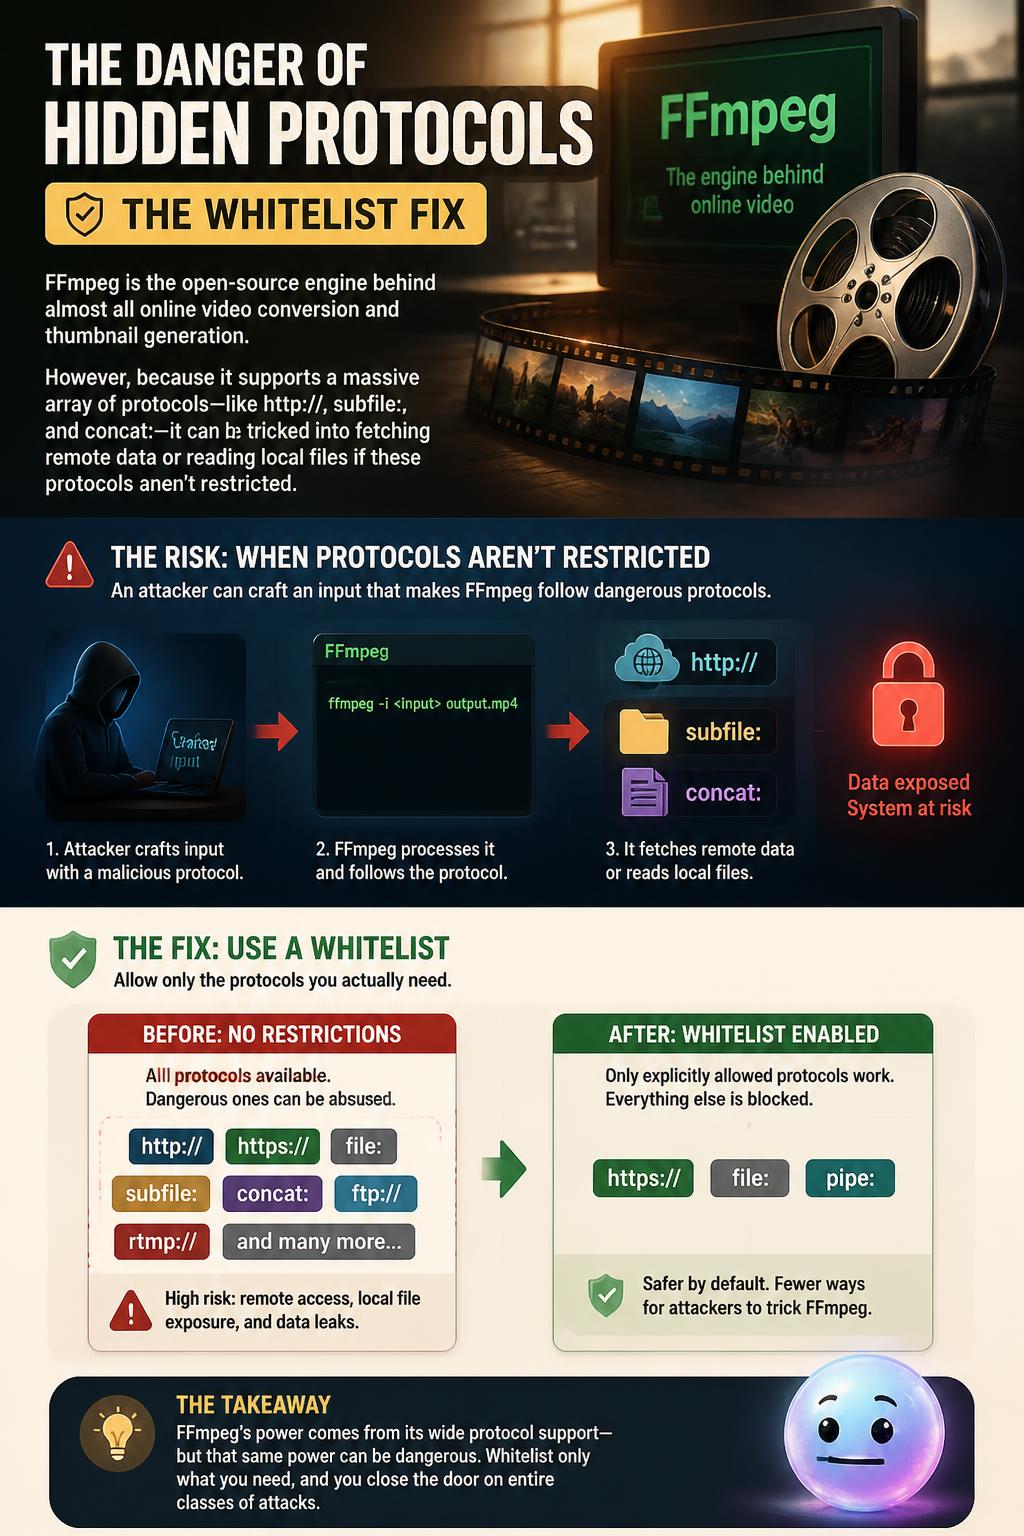
007skaty FFmpeg runs most online video conversion, but unrestricted protocols like subfile and concat can fetch remote data and expose local files.
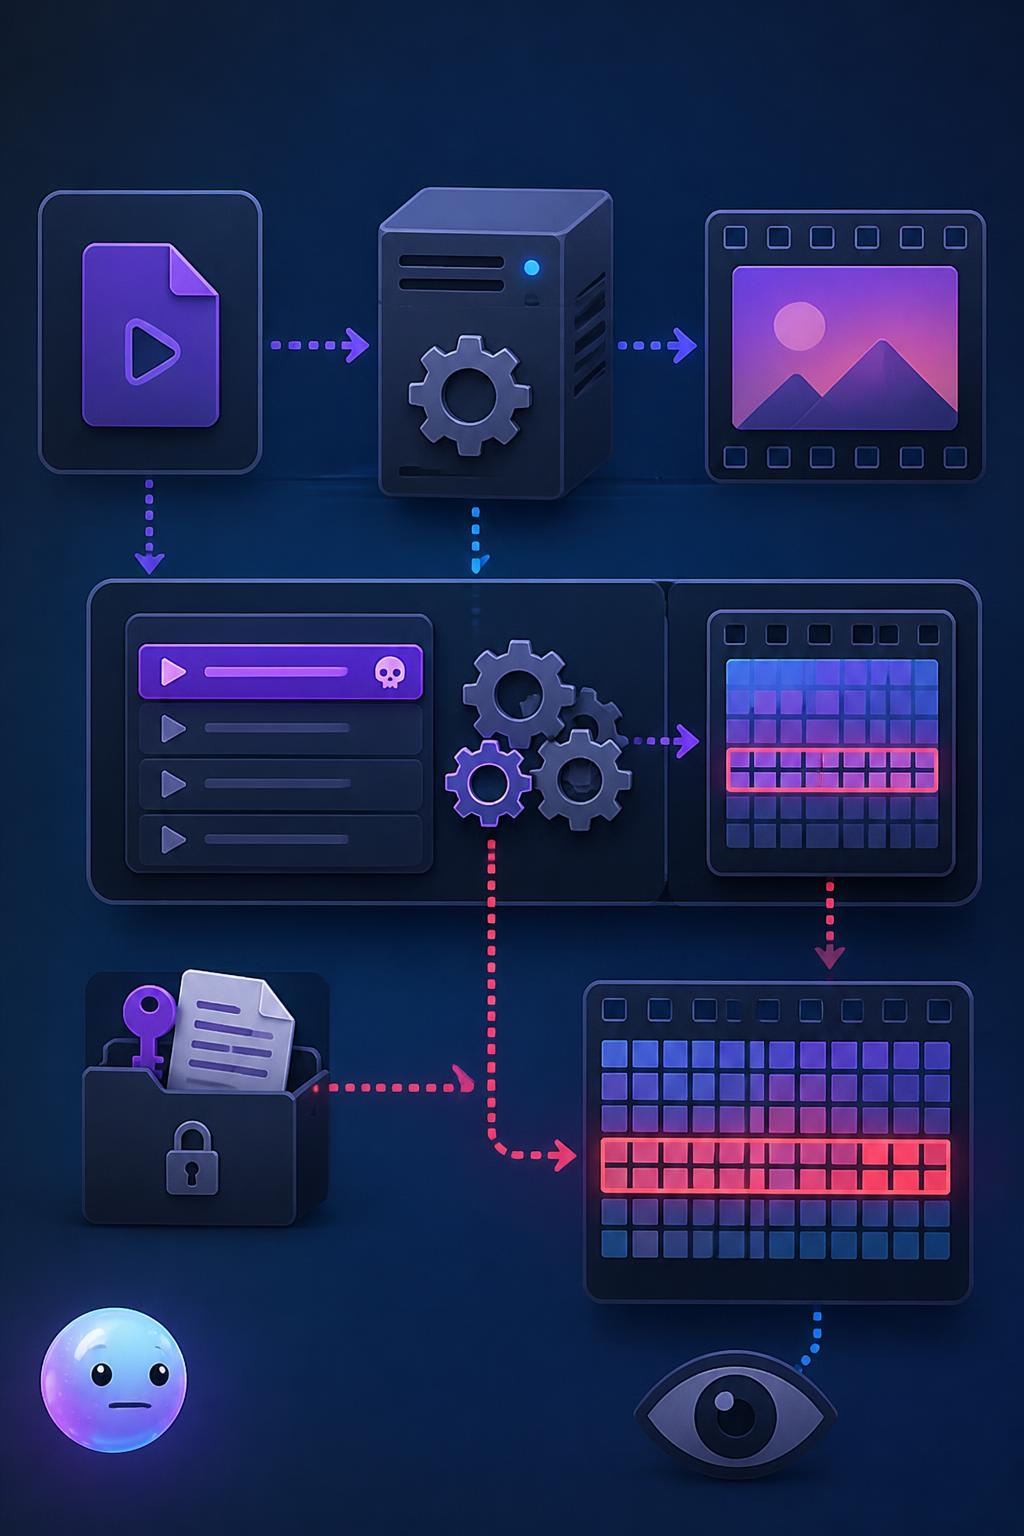
007skaty Whitelisting file formats stops disguised playlists from stealing data during thumbnail generation.
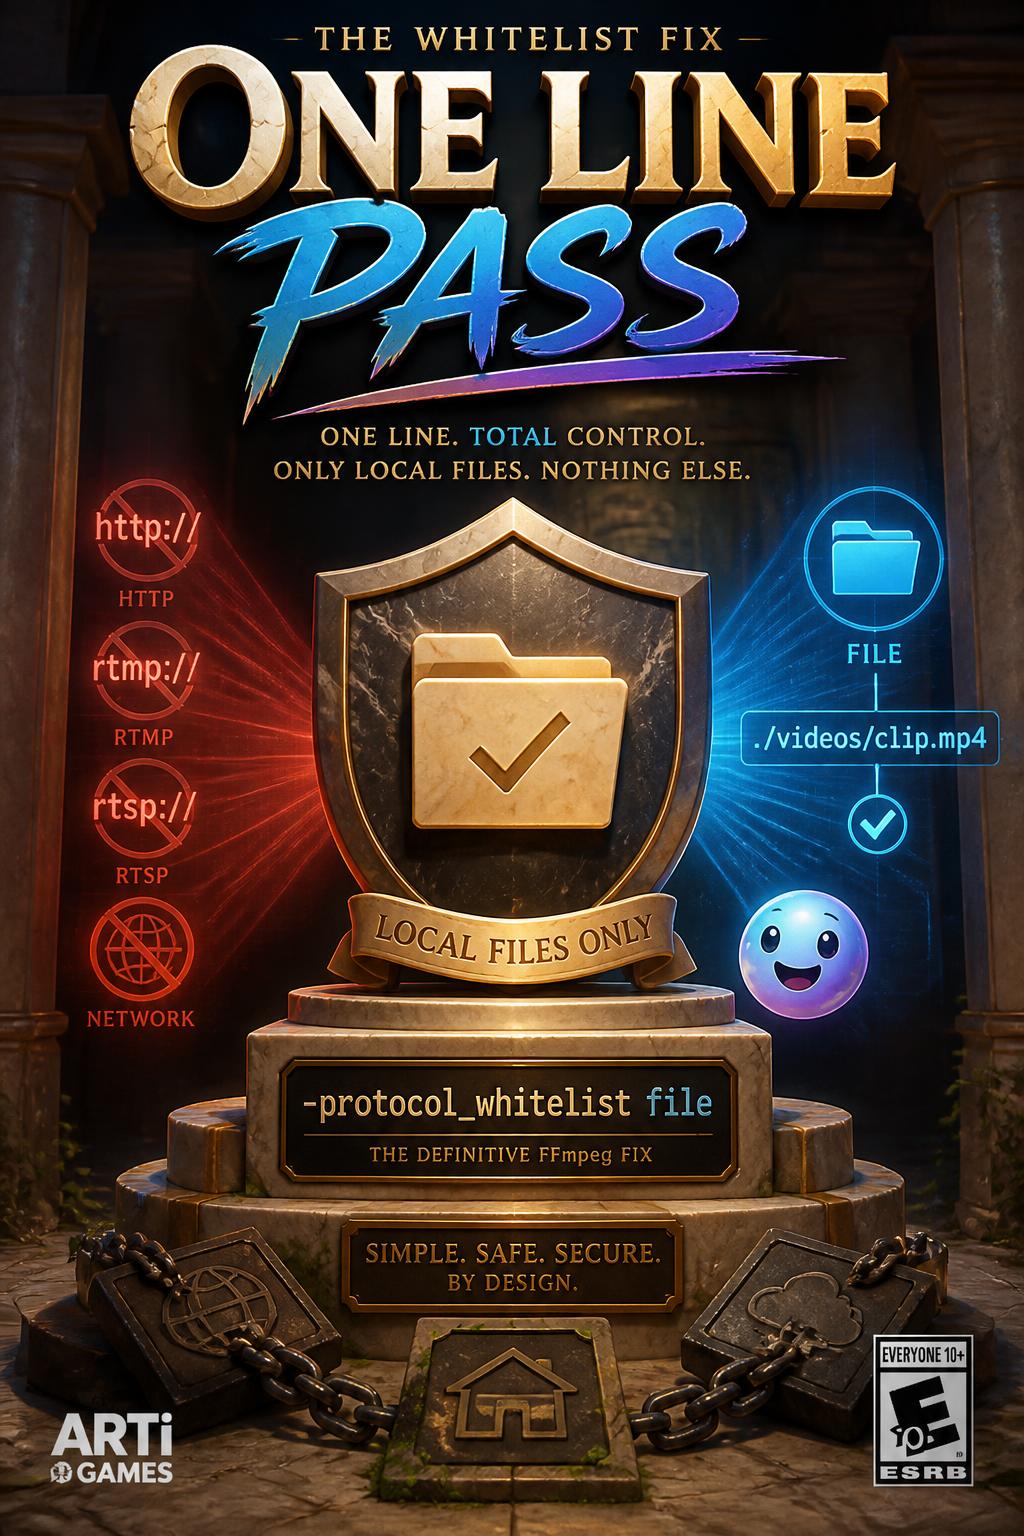
007skaty Draw one continuous line to route approved data to learn how whitelists secure networks.
FFmpeg's massive reach: FFmpeg is so popular that it powers YouTube, Netflix, and even your smartphone's built-in video player.
What is this type of attack called when a server is forced to make unauthorized outbound requests?
How can an attacker use an unrestricted FFmpeg process to steal a server's private files?
What command-line argument is used to restrict FFmpeg to only opening local files?
Why is sanitizing the file path string (like checking if it ends in .mp4) not enough to stop this attack?